
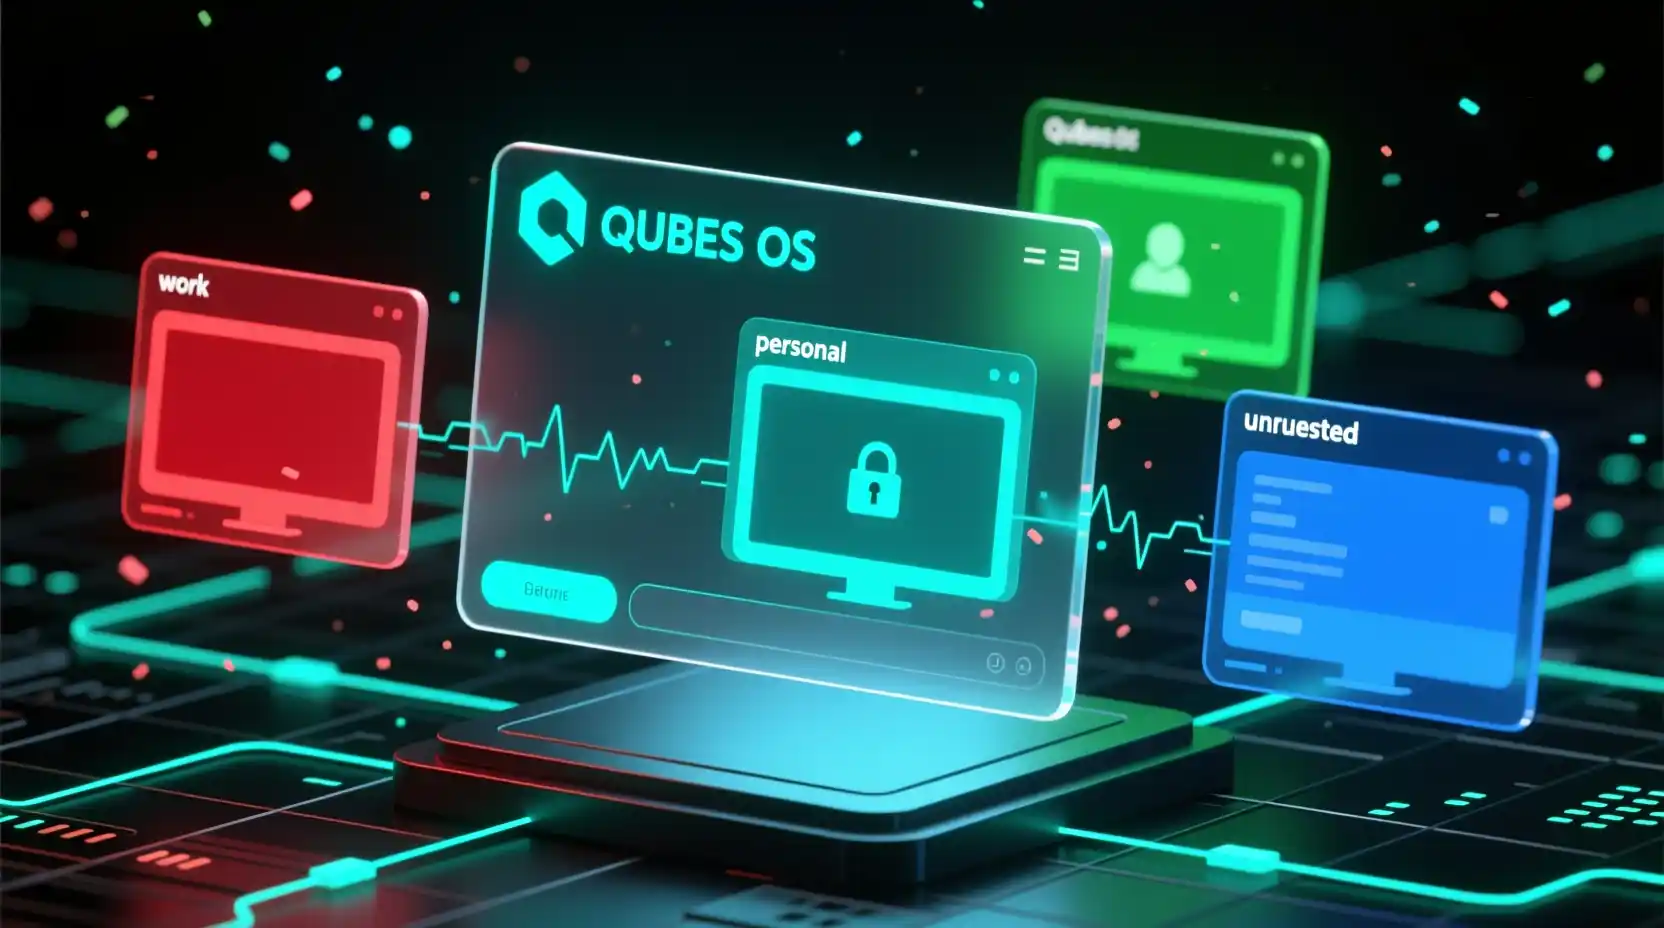
Qubes OS 4.3.0: A Deep Dive into Security-First Innovation
Introduction to Qubes OS
In an era where digital threats loom large, traditional operating systems (OS) struggle to balance usability and security. Qubes OS, a security-focused operating system, redefines this paradigm by leveraging virtualization to compartmentalize tasks and mitigate risks. With its latest iteration, Qubes OS 4.3.0, the platform introduces groundbreaking advancements in security, flexibility, and ease of use. This blog post explores the core features of Qubes OS 4.3.0, focusing on three pivotal keywords: security-first design, granular compartmentalization, and secure virtualization. We’ll also compare Qubes OS 4.3.0 with earlier versions and highlight why it’s a must-consider OS for cybersecurity-conscious users.
- Security-First Design: The Core Philosophy
Qubes OS has always prioritized security over convenience, and version 4.3.0 embodies this ethos with enhanced features. Unlike traditional OSes, which operate as a single monolithic system, Qubes partitions tasks into isolated virtual machines (VMs), ensuring that a breach in one compartment doesn’t compromise the entire system.
Key Improvements in 4.3.0
- Hardware-Level Protection: Qubes OS 4.3.0 now integrates with Intel’s Confidential Computing and AMD’s Secure Encrypted Virtualization (SEV), ensuringing sensitive workloads are hardware-encrypted and isolated from even the hypervisor.
- Automated Threat Response: The new version includes Qubes-Firewall-2, a next-gen firewall that dynamically blocks suspicious network traffic based on real-time threat intelligence (e.g., MITRE ATT&CK patterns).
- Enhanced Template Management: Users can now customize stricter access policies for templates (shared OS images), reducing the risk of malicious code propagation.
Why It Matters
A security-first in a VM like your “work” AppVM won’t affect your “personal” or “shopping” VMs. This isolation-first approach is unparalleled in consumer-grade systems.
- Granular Compartmentalization: Tailoring Isolation
Qubes OS 4.3.0 takes the concept of micro-segmentation to the next level with AppVMs, NetVMs, and Disposable VMs. These tools allow users to create disposable, task-specific environments tailored to their needs.
How 4.3.0 Elevates Compartmentalization
- Custom VM Templates: Users can now create lightweight for specific applications (e.g., a Tor-only VM or a VM for cryptocurrency exchanges), simplifying setup.
- USB Device Control: Enhanced USB3 support lets users restrict USB devices to specific VMs. For example, you can allow a printer in your work VM but block it in all others.
- Inter-VM Communication: 4.3.0 introduces Policy-Based Copy-Paste and Drag-and-Drop controls, preventing data leaks between compartments.
Real-World Use Case
Imagine using a Qubes Disposable VM to test an untrusted software package. Once done, you delete the VM, eliminating any residual malware. Meanwhile, your email and banking VMs remain untouched.
- Secure Virtualization: The Xen Hypervisor Foundation
At its heart, Qubes OS is powered by the Xen Project Hypervisor, which provides the backbone for running multiple VMs on a single machine. Qubes OS 4.3.0 builds on this foundation with critical virtualization enhancements.
Virtualization Upgrades in 4.3.0
- Xen 7.2 Integration: Xen 7.2 brings improved resource allocation and better support for modern CPUs (e.g., ARM64 architecture), ensuring Qubes runs smoothly on both traditional and emerging hardware.
- GPU Passthrough Safety: Users can now securely share a GPU with a VM while sandboxing it from other tasks, making Qubes viable to developers and gamers.
- Automated VM Snapshots: Regular VMs can be backed up automatically, reducing downtime in case of corruption or attack.
What This Means for Users
Secure virtualization means your personal files, work projects, and guest OSes live in isolated “containers,” drastically reducing the attack surface. Even if a VM is compromised, the rest of the system remains secure.
Comparing Qubes OS 4.3.0 with Earlier Versions
To highlight the advancements in 4.3.0, let’s compare it with Qubes OS 4.2.0 using a detailed table:
| Feature | Qubes OS 4.2.0 | Qubes OS 4.3.0 |
| Xen Version | Xen 7.0 | Xen 7.2 |
| USB3 Support | Limited, requires manual setup | Native USB3 with VM-specific rules |
| Firewall Capabilities | Rule-based | Dynamic threat-integrated |
| VM Templates | Basic templates | Customizable, app-specific |
| GPU Passthrough Security | Experimental | Production, with Xen 7.2 isolation |
| Disposable VMs | Yes | Enhanced with snapshot rollback |
| Hardware Encryption | No | Supports Intel/AMD secure features |
| USB Device Policies | Global rules only | Per-VM restrictions |
Who Should Use Qubes OS 4.3.0?
Qubes OS is ideal for:
- Security Professionals: For penetration testing and threat modeling.
- Privacy-Conscious Users: To isolate sensitive tasks (e.g., banking, email) from web browsing VMs.
- Developers: For secure code testing with disposable VMs.
- Journalists/Whistleblowers: To protect sources and sensitive data.
Technical Considerations Before Installation
- Hardware Requirements: Qubes OS requires a 64-bit x86 CPU with VT-x (Intel) or AMD-V support.
- Disk Space: Allocate at least 40GB for the base system, plus 10–20GB per AppVM.
- Learning Curve: Expect a steeper setup process compared to mainstream OSes, but extensive documentation is available.
Conclusion: Is Qubes OS 4.3.0 Right for You?
While Qubes OS 4.3.0 may not be the easiest OS to learn, its unmatched security model makes it a fortress for users who prioritize privacy and data protection. By combining on security-first design, granular compartmentalization, and secure virtualization, Qubes turns the tables on adversaries, making breaches exponentially harder.
Whether you’re a privacy advocate, a security researcher, or simply tired of digital vulnerabilities, Qubes OS 4.3.0 is a bold step toward reclaiming control over your digital life.
Disclaimer
This blog post is for educational and informational purposes only. Qubes OS is a powerful tool, but it requires careful configuration and understanding of its features to achieve maximum security. The author and publisher are not liable with or endorsed by the Qubes OS project or its contributors. Readers are advised to perform their own evaluations, consult cybersecurity experts, and follow best practices for digital security. Use of Qubes OS should not be considered a substitute for comprehensive security strategies, including regular software updates, strong passwords, and user awareness. The author assumes no responsibility for any misuse, inaccuracies, or damages resulting from the content of this article.
Have any thoughts?
Share your reaction or leave a quick response — we’d love to hear what you think!
-
 0
-
 0
-
 0
-
 0
-
 0
-
 0
